Overview
The Mission Is the Missing Abstraction defined the object. This closer turns the architecture into a build plan, and the plan opens with a choice, because the estate a deployment already runs picks its entry point. The benefit is write access you can defend, and the entry point sets how soon a deployment can claim it, since the OAuth binding gates issuance from the first bundle while a standalone Mission Authority Server makes no prevention claim until PEP and PDP coverage arrives or an Authorization Server redeems its issuance grants. After the entry point is chosen, the Mission Assurance Levels the repository publishes order the adoption bundles. The maturity and status claims in this part are as of October 25, 2026 and follow the editor’s copies, and the Reference carries the reconciliation date the handbook tracks. The concluding chapter, Weighing Mission-Bound Authorization, covers substrate independence, the five bindings, and the trade the standalone Mission Authority Server makes.
The binding is a separate axis from the levels, and the standalone Mission Authority Server is a peer entry point the estate can choose at any level. The entry point and the levels make up the build plan. The second half of this part covers what surrounds it: the ecosystem a Runtime-Enforced deployment composes with, the roadmap beyond it, the operational surfaces you will own, and the pieces the community still has to standardize.
Choose the entry point
The estate a deployment already runs decides where it starts, and four questions read the estate:
- Can you change issuance? An Authorization Server you can extend, with Pushed Authorization Requests (PAR), Rich Authorization Requests (RAR), and JWT access tokens, can become the Mission Issuer. A shared, third-party, or SaaS Authorization Server cannot.
- Can you mediate consequential actions? Action-time enforcement needs a policy enforcement point (PEP) on each consequential path, at a gateway, an MCP server, the harness, a credential broker, or the resource itself.
- Must governance span several Authorization Servers? One governance point over many Authorization Servers is the job of a standalone Mission Authority Server (MAS), with each consuming Authorization Server redeeming the issuance grants it mints.
- What revocation delay and enforcement coverage can you claim? Issuance gating bounds revocation by the token lifetime, and runtime enforcement covers only the paths a PEP mediates, so the first three answers set the claim.
Who issues
The Architecture’s entry ramps turn the answers into an entry point. The issuer is chosen per Authorization Server or credential plane, and one Mission Authority Server can govern many:
| Your estate | Who issues | What you build first | What carries the enforcement | What you can claim first |
|---|---|---|---|---|
| An Authorization Server you can change, with PAR, RAR, and JWT access tokens | The OAuth binding. The Authorization Server is the Mission Issuer and gates issuance on Mission state | Intent intake, derivation, approval, the record, and state-gated issuance at the Authorization Server, and a Mission-creating client that submits Intents through PAR. Resource Servers stay unchanged | Issuance gating, plus PEPs on the runtime-enforced paths | Approved-record integrity and revocation bounded by the token lifetime, at the grain each Resource Server already enforces |
| An Authorization Server you can change, but RAR is absent or tokens are opaque | A MAS first, and the OAuth binding once the Authorization Server gains the token plane, as a peer move | A MAS beside the Authorization Server, with approval integration and Mission correlation. Tokens stay unchanged | PEP coverage alone, with the policy decision point (PDP) joining each token to its Mission at the point of use, or verifying a Join Assertion (a MAS-signed statement binding one sender-constrained token to its Mission) | Approved-record integrity and audit. Prevention waits on PEP and PDP coverage with a trustworthy join to the Mission |
| An Authorization Server you cannot change (shared, third-party, SaaS) | A standalone MAS, phase by phase | Records and approvals | PEP coverage alone until the Authorization Server, or its vendor, adds issuance-grant redemption. After redemption, grant minting gates issuance as in the many-servers row, with the same exposure | Approved-record integrity and audit, with no prevention claim until PEP and PDP coverage arrives, and then action-time enforcement only on the paths it covers |
| A credential broker | The broker, with the Authorization Server or the MAS holding the Mission record | The broker keeps custody and mints short-lived leases as before, now gated on Mission state. A lease carries the mission claim where its minting conforms to a Mission-binding profile, for example by redeeming issuance grants as a consuming Authorization Server, and otherwise carries the Mission identifier by other means and is Mission-referenced, as the binding’s editor’s copy reserves the claim | The broker as the issuance chokepoint for its own credentials, plus PEPs at action time on the runtime-enforced paths | Issuance gating for the broker’s own credentials. Credentials obtainable outside the broker need their own coverage and do not inherit that claim |
| Many Authorization Servers, one governance point | A MAS as the estate control plane, with an issuance join at each consuming Authorization Server | The MAS, then issuance-grant redemption at each consuming Authorization Server. Current-state gating at redemption and refresh is an additional integration | MAS grant minting is state-gated. An Authorization Server with the integration also checks current state at redemption and every refresh, and one without it issues no refresh tokens. PEPs enforce at runtime only on the paths they cover | Approved-record integrity across the estate. Revocation at an Authorization Server without the integration is bounded by the access-token lifetime plus the grant’s remaining redemption window, which The Authority Control Plane prices in full |
| No PEP or PDP over consequential paths | The OAuth binding where the Authorization Server allows it, and the runtime layer where an action class needs it | Lifetime-bounded reliance: short tokens and gated refresh | Issuance gating alone | Revocation bounded by the token lifetime on gated paths, and no action-time claim for the high-consequence classes until the runtime layer covers them |
Every row shares the record, the integrity anchors, and the lifecycle, so a Mission carries unchanged from the row a deployment starts on to any row it adds later.
The levels then order the work. Under the OAuth binding, Baseline Issuance comes first, the Runtime-Enforced level follows on the paths where an action class needs a per-action decision, and the Governed Agent and High-Assurance Agent bundles follow where the risk warrants them.
The adoption sheet
The sheet is the OAuth-binding implementation sequence. Its bundles are cumulative, each including the one before it, and a deployment adopts the bundle its risk warrants and stops there. With a standalone MAS, the Baseline column’s Authorization Server changes do not apply. The MAS holds the record and the lifecycle, the Authorization Server stays unchanged, and a path becomes enforced only with the Runtime-Enforced column’s PEP and PDP coverage plus a trustworthy join to the Mission. The MAS deployment gets the Baseline column’s issuance kill switch only through the issuance grant. Claims apply to the paths a deployment governs, with issuance gating on some paths and runtime enforcement on others (not every resource checks Mission state).
| Baseline Issuance | Runtime-Enforced | Governed Agent | High-Assurance Agent | |
|---|---|---|---|---|
| What changes, and who owns it | The Authorization Server’s owner adds Intent intake over Pushed Authorization Requests (PAR), derivation and the approval event, the integrity anchors, the mission claim, and state-gated issuance and refresh, and sizes token lifetime to the staleness the deployment tolerates. The Mission-creating client submits Intents. Resource Servers change nothing. A Resource Server that authorizes only from scope is served only where the Authorization Server establishes a safe scope projection for it (Baseline Issuance) | The owner of each consequential boundary (gateway, MCP server, harness, credential broker) adds a PEP, and a PDP evaluates each action over the AuthZEN profile. The Mission Issuer serves Status (or introspection) with a published staleness bound, and decision and execution records join on the Mission id. Resource Servers a PEP fronts still change nothing | The approval surface records Consent Evidence of what the Approver saw. The harness gates every resume and cached connection on Mission state. Child Delegation and Expansion, with the experimental Orchestration and Discovery, join as needed | The credential broker holds the sender-constraint key as the mediating PEP. Approvals for the high-consequence classes become action-bound and render in a component isolated from the agent. The state source runs active freshness, and the deployment declares and audits a path scope with no unmediated path and attests its Enforcement Scope Statement. Trifecta containment adds least exposure, the enforced harness taint rule, and mediated egress over enumerated channels |
| You can then grant | Consequential reads and writes outside the high-consequence classes whose bounds the receiving Resource Server enforces, attributable and killable at the issuance gate; outstanding tokens run to their own expiry or the next introspection | Consequential actions that need a per-action decision: parameter-bound writes and bounds finer than the receiving Resource Server enforces | Unattended operation and delegation (the overnight agent and the sub-agent), with Consent Evidence binding each human approval, including the standing consent unattended instances run under | The high-consequence classes (irreversible actions, external commitments, and privileged administration), under mediated custody and action-bound approval |
| What you get | Approved, integrity-bound Missions, state-gated token issuance, and a possession-independent kill switch for future derivation | Per-action PEP/PDP enforcement, current Mission-state checks, and a published freshness bound for revocation | Approval evidence, session-continuity stop, sub-agent containment, and tamper-evident audit where adopted | The agent-compromise-resistant claim (a compromised agent cannot present the credential or reach a mediated action without a fresh independent approval) and, where claimed, trifecta containment (an injected agent cannot egress on the strength of untrusted content alone) |
| What stays outside | Action-time defense, prompt revocation of already-issued tokens, safe unwinding | Full consent-rendering evidence, runtime harness binding, orchestration unwind (experimental) | Proof that every possible side channel has been mediated: the deployment still defines its enforcement scope | Protection inside the approved scope: a compromised agent can still misuse authority the Mission grants, which is why scope stays tight |
| Acceptance test | Revoke a Mission by mission_id through an authenticated means independent of possession of any token, such as Status’s “Mission Lifecycle, revoke only” conformance class or a deployment-defined surface. Refresh and new derivation are then refused, and no outstanding token outlives the published lifetime or the Mission’s expiry. Issuance to a scope-only target with no safe projection is refused. A bare client-supplied Mission identifier binds nothing. intent_hash and authority_hash reproduce from the record alone | Revoke a Mission and watch the next consequential action fail closed within the published freshness bound. Then pull the Mission id and reconstruct the whole story: the approval, the derived authority, the decisions including denials, and the revocation | Revoke a Mission while its agent is idle and watch the harness suppress the next resume. consent_rendering_hash reproduces from the recorded disclosure | From the agent’s own process, attempt a mediated high-consequence action directly, then through the broker without a fresh action-bound approval: both fail. For trifecta containment, inject untrusted content and attempt egress to a destination the Approver did not name: refused |
The Baseline tests come from the Architecture’s verification guidance, the Runtime-Enforced test is the handbook’s running example run against your own deployment, and the Governed and High-Assurance tests restate those levels’ proof obligations as checks.
The Architecture defines each Mission Assurance Level as an adoption bundle, a named set of documents taken in the order deployments build them. A level is guidance, not a conformance class or a rank to reach. A relying party compares the assurance claims a deployment can show (approved-record integrity, bounded revocation latency, action-time enforcement, parameter-bound enforcement, transaction-grade execution, and the named high-assurance claims), not its level. The “You can then grant” row is informative. A level does not determine any action class’s containment property, and what a level grants varies with the binding.
The documents follow the family manifest’s reference stacks. As a deployment requirement, the minimum interoperable implementation is the first six rows, the Architecture’s reference security architecture. For issuance alone, it is the OAuth binding.
| Document | Required from | Why it is in the bundle | What it rests on |
|---|---|---|---|
| The OAuth binding | Baseline Issuance | The record, the integrity anchors, the mission claim, and state-gated issuance: what every other piece joins on | Published RFCs, plus OpenID Connect Core for its approval-authentication parameters and the openid scope rule, though it requires no AS to support OpenID Connect. It cites three Internet-Drafts normatively, each only for an optional capability: the OAuth working group’s RAR metadata remediation draft for the remediation challenge, and two proposed individual drafts, the Actor Profile for Delegation and Client Instance Identification for the instance-context composition |
| Substrate Requirements | Runtime-Enforced | The kernel the runtime and AuthZEN documents consume normatively | Ratified specifications |
| Mission-Bound Runtime Enforcement | Runtime-Enforced | The decision contract: action classes, the PEP/PDP split, parameter binding, and fail-closed behavior | Ratified specifications |
| Its AuthZEN profile | Runtime-Enforced | The wire between PEP and PDP, so enforcement points and decision points from different vendors interoperate | The AuthZEN Authorization API 1.0 (Final, January 2026); the Access Request and Approval Profile (ARAP) and the Obligations Profile, OpenID AuthZEN working-group drafts; and Client Instance Identification, a proposed individual draft. Within the family it also cites Runtime Evidence normatively, plus Capability Binding and the harness where a deployment adopts them, and it cites the RAR metadata remediation draft only informatively. The external drafts are where the remaining dependency risk sits |
| Mission Runtime Evidence | Runtime-Enforced | The Decision and Execution Records the AuthZEN profile consumes, joined on the Mission id | Ratified specifications |
| One freshness source: Status (the reference choice), issuer introspection, or Signals | Runtime-Enforced | Current Mission state for the PDP within a published staleness bound. The handbook’s advice is to start with Status and add the Signals push once the polling is sized | Ratified specifications (introspection is RFC 7662) |
| Consent Evidence | Governed Agent | Proof of what the Approver saw, not only what was approved | Ratified specifications |
| Mission-Aware Agent Harnesses | Governed Agent | The session-continuity stop: work ends when the Mission does | Ratified specifications |
| Child Delegation and Expansion, with the experimental Orchestration and Discovery | Governed Agent, as needed | Delegation, governed growth, unwinding, and runtime discovery, when the deployment needs them | See the catalog |
High-Assurance Agent adds no documents. It is a claims level, and the runtime profile fixes both claims’ obligations. Each claim requires execution-environment attestation of the Enforcement Scope Statement, so the claim is technical rather than organizational, while base runtime conformance requires no attestation. Beyond the manifest’s stacks, this handbook also adopts at Baseline the Architecture, as the front door, and the Resource Access Profile, which every example uses, and at Runtime-Enforced the runtime’s OAuth 2.0 profile, which maps a validated Mission-bound access token onto the runtime’s inputs. The family is proposed individual Internet-Drafts. Two are on the IETF datatracker: the OAuth binding as draft-mcguinness-oauth-mission-01 and the Resource Access Profile as draft-mcguinness-oauth-mission-resource-access-00. The rest are editor’s copies, and none is adopted by a working group. No production Mission deployment is known on any binding.
On the MAS entry point, the standalone Mission Authority Server is a controller over the OAuth binding’s Mission data model whose package brings the OAuth binding and Status. The MAS serves Status and the lifecycle verbs itself, is the freshness source, and, where it claims the optional Expansion and Child Creation capability, hosts expansion and Child Mission creation on its own submission surface.
The read-only ceiling
In most estates, agents run read-only, a human
approves or executes every write, and the deployment is a pilot with no
path to graduate. That posture is rational. In July 2025 a coding
agent deleted a production database
during an explicit code freeze, against instructions repeated in
capital letters, and the story traveled because every enterprise
recognized the shape. On the published accounts, the credential the
agent held permitted the deletion it performed. A probabilistic model on
standing credentials has no stateable blast radius. Organizations can bound one today by connecting approved work to policy, credentials, and execution in their own integrations, but the standard stack offers no interoperable form for that connection. The ceiling is a context problem. The layer deciding each call cannot see the undertaking, so it cannot price a write. The same deletion is catastrophic or routine depending on the approved work around it, and a context-free stack has to price for catastrophic every time. Task-grain context is what changes the arithmetic, so the graduation path below runs through the approved task rather than through better model behavior. Under the OAuth binding, Baseline Issuance prices the write at approval. The credential carries only authority derived from the task, so a Resource Server that enforces the token’s authorization_details, or a scope the Authorization Server safely projected from them, already enforces the task’s bounds. The Runtime-Enforced level prices it per action, against current Mission state, for the bounds the Resource Server cannot check. The posture is also expensive, and each compensating control costs more than it looks:
| Today’s control | What it costs | What retires it |
|---|---|---|
| Read-only scoping | The value ceiling. The reads are not safe either, because an agent can be steered by anything it was allowed to see, and everything it holds can leak (least exposure) | Authority right-sized from the approved task, with exposure bounded as deliberately as action |
| A human approves or executes every write | Approval fatigue at the scale where agents are useful, and the human becomes the unmediated enforcement point | Approval at Mission grain, human where the class demands it, machine-speed permits per action (runtime enforcement) |
| The permanent pilot | The sandbox never graduates, and shadow paths grow around it | A named enforcement scope and the assurance claims the deployment can show |
The ceiling also has an infrastructure reading. It is what operating without a control plane feels like. Nothing holds a bounded desired state to reconcile the work against, so the only safe posture is denying the data plane its writes. The levels below are the graduation path off this ceiling. What was managed for human delegates by judgment, deterrence, and accountability has to be built for agents as architecture, and this part is that architecture in adoption order.
You do not need an agent to start
Nothing in the object requires the actor to be a model. The card chapter runs five posts of mission-based authorization with no agent in sight, because expense governance is the pattern applied to humans, and the protocol version works the same way. A Mission bounds the judgment inside it the same way whether a model or a person exercises it.
That makes human access the natural first deployment, and a better outcome than the one traditional IGA produces. Start with access requests. The request rides the approval workflow the organization already staffs (Deferred Approval is deliberately shaped like an IGA review), and what comes out the other side is not a standing entitlement waiting for the next recertification campaign but a bounded, self-terminating, evidence-joined grant: authority sized to the task, expiring with it, attributable through it. Access reviews shrink toward the ceilings and the exceptions, because a grant that expires with its task needs no later review.
A Mission also scales down. One resource, one approver, and one afternoon make a well-formed Mission, and the machinery costs what the task warrants (synchronous approval, no delegation, and no per-action gate beyond issuance if the class does not demand one). A use case falls outside the model only when there is no task, where the credential lifetime is the work.
And the actor does not need to be new. The estate already runs
standing agents that nobody calls agents: the CI pipeline that deploys
on merge, the Terraform apply that reshapes infrastructure, the RPA
bot filing what humans used to file, the Kubernetes operator
reconciling all night, the scheduled job that moves money on the first
of the month. Every one of them is long-running delegated work on
standing credentials sized for the integration rather than the task,
and every one qualifies for the same machinery for the same reason the
agent does: the work outlives the request, and the authority should be
bound to the work. Such a job gets its Mission from an administrator,
who approves it over the job’s own service_owned authority or an
organizational policy, or from a policy version a human approved,
which activates it under governed_policy (a high-consequence job, such as one that moves money, only through a committed exception that names the class, as who may approve sets out). Mission-based authorization is a primitive for delegated work of any kind, and the probabilistic
agent is the actor that made the gap impossible to keep ignoring.
Humans make forgiving first users of the rails (they tolerate latency, they answer clarifying questions, and they do not get prompt-injected), so agents can inherit issuance, enforcement, and evidence already proven on human traffic. The estate that governs human task access with Missions today has already built the delegated-authority control plane its agents will need tomorrow.
Not every resource checks Mission state
Start with a path whose bounds your existing resources already enforce. Add the approved Mission record and gate credential issuance on its state. Add runtime checks where a path needs finer constraints, faster revocation, or the controls its action class requires. A path is the route by which a credential is obtained and an action reaches a resource, including the enforcement boundaries it crosses, so a gateway-mediated call and a direct call to the same resource are different paths. Claims are held per path, and the enforcement-scope statement records which paths run which shape and which stay outside Mission enforcement.
Issuance gating needs a Mission-aware Authorization Server, an integrated credential broker, or an Authorization Server that redeems Mission Issuance Grants (who issues).
| Deployment shape | What changes | What it establishes |
|---|---|---|
| Issuance-only | One of those issuers gates the credentials it issues on Mission state. The resources already enforce the scopes, authorization details, and constraints they receive | Approved-record integrity and a worst-case bound on how long issued authority survives revocation. No action-time Mission check |
| Runtime-enforced | A PEP holds each action until a PDP, over the AuthZEN profile, permits it against the Mission’s current authority and state, read from a state source with a published staleness bound. The PEP sits wherever it can enforce the required constraints without bypass: a gateway, an MCP server (the MCP application post), the harness for the local effects and resumes no gateway sees, a broker, or the resource itself | Action-time enforcement on the declared paths and classes, with parameter binding where the class requires it. Resources behind a suitable PEP can stay Mission-unaware |
Neither shape replaces the systems the estate already runs. The identity provider keeps authenticating subjects. IGA keeps the standing entitlements that bound every Mission from outside (coexistence). Gateways, MCP servers, harnesses, and credential brokers keep their jobs and add a PEP or a Mission-state check only on governed paths. Standing service accounts stay until each recurring job moves to a Mission, and Mission state does not revoke a service account’s own grant while the job still uses it. A client must not present an ordinary token it already holds for a Mission’s task unless a trusted enforcement path establishes that Mission for the request, and in the editor’s copy an AS issues no token outside a Mission, on any grant type, for a Mission-governed resource.
The action class sets the minimum. The high-consequence classes (irreversible actions, external commitments, and privileged administration) need runtime enforcement with active freshness, parameter binding, reverification, and evidence. A path that carries them without those controls cannot claim action-time enforcement for them, and its enforcement-scope statement records that class as unenforced on that path. Below that floor, issuance gating is enough where the receiving resource already enforces the approved bounds and the revocation delay is acceptable. A risk signal may tighten or refuse, and it never enlarges authority or bypasses the classification floor (the adversary model).
Publish the worst-case revocation bound for each path. Issuance-only paths account for the credential lifetime and the age of any older state observation used at minting, including a delayed grant redemption. Runtime paths account for state freshness, permit validity, and execution under the freshness rules. Mediated custody does not remove those windows. The Status profile counts token lifetimes sized to the tolerated staleness as a propagation mechanism, and the Reference’s revocation matrix prices each setting.
For example, an estate can gate issuance for a reporting path whose existing resource enforces the approved scope, add a PEP to payments operations that need action-time checks, and keep a third integration explicitly outside Mission enforcement. The scope statement records all three. Adding the payments PEP changes nothing at the reporting resource and does not improve the excluded integration’s claim.
Baseline Issuance
Under the OAuth binding, Baseline Issuance is the issuance profile alone, the Baseline column of the adoption sheet plus the subset rule on every derivation. This is The Mission Is the Missing Abstraction and the OAuth binding.
Its deployed shape is what the Architecture calls the issuance-only deployment. The draft repository includes a reference implementation built on the OAuth binding, with a requirement-level conformance ledger, and an issuance-only reference deployment of this shape (a Mission-aware AS and Resource Servers that need not be Mission-aware), accepted as a bounded reference deliverable. It also carries a runtime composition and a Mission Authority Server pilot. None of the three deployments is a conformance, production-readiness, or interoperability claim.
Two points the sheet’s Baseline column compresses: short-lived tokens turn the issuance stop into a real bound, since revocation reaches every issuance-gated path within the token lifetime with no resource changing at all, and audit joins on one identifier. The what-not-to-claim list keeps a Baseline Issuance deployment from claiming the checks it lacks. Under the OAuth binding it is the right first quarter.
A Resource Server that authorizes only from scope operates within the Mission only where the Authorization Server establishes a safe scope projection, a trusted mapping under which the scope a token carries grants that target no more than the token’s authorization_details. The Authorization Server refuses issuance to a scope-only target when it cannot establish one. In the editor’s copy, where a resource is Mission-governed (the deployment classifies it so, or authenticated protected-resource metadata declares mission_bound_authorization_required), the Authorization Server issues tokens for it only under a Mission, on any grant type, and refuses any other token request for it with invalid_target.
For many enterprises the first agent-credential control already shipped is a credential broker: real credentials moved into a vaulted plane, with agents holding just-in-time, short-lived, sender-constrained leases (CB4A, an individual draft that has since expired, is the spec-shaped instance). If that is your starting point, Baseline Issuance starts from an asset rather than zero, one integration away, as the credential-broker row of who issues sets out. The chokepoint you already deployed becomes the issuance gate, the kill switch reaches every future lease, and the broker’s ledger joins on mission_id. The broker cannot supply the object on its own, because a lease is not the task (the landscape’s broker row).
The Runtime-Enforced level
The Runtime-Enforced level is where action-time enforcement arrives, and it is a substantial build, not a wedge, measured from the runtime profile’s conformance section. Two additions:
- Put a PEP at each consequential boundary the enforcement scope covers, and adopt the runtime contract with its AuthZEN profile. The PDP evaluates each action against the live Mission, parameters bound, failures closed, and an action governed by a consumption bound the deployment does not meter refused (the metering itself is the Evaluate-only Consumption Metering profile). This is Mission-Bound Runtime Enforcement, the runtime draft with its OAuth 2.0 profile, the AuthZEN profile, and Mission Runtime Evidence.
- Serve Status as the freshness source. Revocation is only as fast as consumers learn it. The signed pull surface (or issuer token introspection) is the Runtime-Enforced half of Mission Lifecycle and Change, and it is what makes “only
activepermits reliance” operational. Where a revocation must bite in seconds, size the polling to that bound.
For AI agents, the Governed Agent bundle’s additions should come with this level: Consent Evidence and the harness, because an agent’s approval surface and its resume path are where the guarantees otherwise lapse (From a Request to an Approved Mission, The Agent Runtime and Audit).
The first design decision is the enforcement scope: which resources, action classes, and execution paths you can mediate. A deployment that cannot prevent an action on a path must not claim runtime enforcement for that path.
The whole level compresses into one recipe:
| The minimal enforced deployment | |
|---|---|
| 1 | The Mission Issuer records the approved task |
| 2 | Each request reaches its Mission: a Mission-bound token carries the reference, or the enforcement boundary joins an ordinary token to its Mission |
| 3 | A PEP gates each consequential action |
| 4 | The PDP checks action, parameters, actor, and current Mission state |
| 5 | Status (or issuer introspection) provides fail-closed freshness |
| 6 | Evidence joins on the mission id |
The recipe has two shapes, and they differ in what connects a request to its Mission:
| Deployment | What connects the request to the Mission |
|---|---|
| The OAuth binding | A Mission-bound credential, issued state-gated by the Authorization Server that holds the Mission |
| The standalone Mission Authority Server | An ordinary credential from the unchanged Authorization Server, joined to its Mission at the enforcement boundary. The client or a trusted harness names the Mission in the Mission-Reference HTTP request field (identifier id) or in the Mission reference in MCP params._meta (identifier mission_id). The reference is a selection channel only and carries no state or authority. The PEP passes it to the PDP, which binds the token to the Mission through a mapping join or a Mission Join Assertion and denies a failed join as mission_binding_failed |
With the OAuth binding, each edge numbered by the row it implements:
intent_hash, authority_hash,
state, termination")] ST["Status surface
(or issuer introspection)"] end subgraph EB["Enforcement boundary"] PEP[PEP] PDP[PDP] end RS[Resource Server] EV["6. Evidence,
joined on mission_id"] AP -->|"1. approves the task"| M M -->|"2. Mission-bound token:
mission id + issuer,
state-gated"| AG AG -->|"3. each consequential action
+ parameters"| PEP PEP -->|"4. evaluate action, parameters,
actor, current Mission state"| PDP PDP -->|permit / deny| PEP PEP --> RS M --> ST ST -.->|"5. fail-closed freshness"| PDP M -.->|lifecycle events| EV PDP -.->|decisions| EV PEP -.->|executions| EV
With a standalone Mission Authority Server, the record and the lifecycle are the same, but the MAS derives no tokens:
(unchanged)"] subgraph MAS["Mission Issuer: the standalone MAS"] M[("Mission record
intent_hash, authority_hash,
state, termination")] ST["Status surface"] end subgraph EB["Enforcement boundary"] PEP[PEP] PDP[PDP] end RS[Resource Server] EV["6. Evidence,
joined on mission_id"] AP -->|"1. approves the task"| M AS -->|"2. ordinary token,
no mission claim"| AG AG -->|"3. each consequential action
+ parameters"| PEP PEP -->|"4. evaluate, naming the Mission
(the PDP joins the token to it first)"| PDP PDP -->|permit / deny| PEP PEP --> RS M --> ST ST -.->|"5. fail-closed freshness"| PDP M -.->|lifecycle events| EV PDP -.->|decisions| EV PEP -.->|executions| EV
In this shape the permit rests on the join, and revoking the Mission stops nothing at the token layer, so enforcement depends entirely on PEP coverage. Issuance gating returns only through the issuance grant, which the MAS mints for an active Mission and the estate’s Authorization Server redeems for Mission-bound tokens (who issues).
These are six deployment surfaces, not six laws. They are how the five laws become checkable in production: a durable object, derived authority, bound credentials and decisions, runtime containment, lifecycle freshness, and attributable evidence. The recipe does not prove every side channel is mediated, does not make the agent’s reasoning trustworthy, does not unwind completed actions, and does not give cross-domain proof by itself. Those are governed-agent and advanced controls.
Wherever the PEP lands, it has to sit at the last controllable boundary before the effect. An orchestrator check does not replace a resource PEP for a resource the agent can reach directly, and an API gateway does not cover local shell, browser, or file-system effects it never sees. PEP placement and credential custody are separate choices. A PEP at the resource can use the resource’s object-level context, which makes it the strongest placement. A gateway PEP makes custody possible: it can hold the sender-constraint key, so the agent never holds a usable credential for the resource behind it. Neither placement establishes agent-compromise resistance on its own. For the high-consequence classes, that claim requires the custody, approval, freshness, and path-scope controls in the High-Assurance Agent column of the adoption sheet, described in the high-assurance level.
For an interactive starter deployment, do not start with Signals, Deferred Approval and Revision, the Mandate, offline attenuation, cross-domain projection, or SCITT audit transparency. A service-owned workflow with no user present, or a human access request routed to an existing review, is the exception for Deferred Approval. An administrator or the existing review resolves the pending request, so either may need that path from its first useful deployment. Build the recipe above, run it, and let deployment experience tell you which of these you need. The standalone Mission Authority Server is not on that list, because the estate decides it per Authorization Server (who issues).
The acceptance test is the Runtime-Enforced column of the adoption sheet. A deployment that passes both halves can claim runtime enforcement on the paths it tested.
Runtime-Enforced comes before the roadmap for three reasons:
- The issuance floor has the smallest dependency set. Baseline Issuance needs only the OAuth binding and published specifications (OAuth RFCs and OpenID Connect Core). The additional drafts the adoption sheet lists enter with runtime enforcement and do not block Baseline Issuance, and the profiles’ wire details can still change with review, so design against the laws and the architecture rather than the claim names.
- It is the smallest object that closes the named gap. That gap is the translation from mission to authorization requirements that AIMS leaves out of scope, and the Runtime-Enforced deployment is that translation: an approved, integrity-anchored task object, authority derived from it, actions enforced against it, state observable for it.
- The roadmap should follow deployment evidence. The Evaluate-only extensions encode design bets about approval revision, fan-out, and unwinding. Real Runtime-Enforced deployments are what turn those bets into interfaces worth hardening, and the wagers underneath the whole design are named, with their falsifying evidence, in where this could be wrong.
Governed and beyond
After the Runtime-Enforced level come the Governed Agent and High-Assurance Agent bundles, both laid out in the adoption sheet. As at every level, a relying party compares a deployment’s assurance claims, not its level.
The sheet’s “You can then grant” row is how the levels answer the read-only ceiling, each making a broader class of agent work defensible to grant in the runtime contract’s own action classes.
A deployment names the bundle it runs, its enforcement scope, and the assurance claims it can show, and the Reference’s implementation checklist is the checkable form of those claims, down to the sentence a vendor should be able to write.
Composing with the ecosystem
One stack answers where everything sits, from the substrate up, and the standards map (Appendix E) carries the spec-by-spec survey behind it:
| Layer | What sits there |
|---|---|
| Identity substrate | WIMSE (including AIMS) and SPIFFE, with the Actor Profile, Client Instance Identification, and Client Attester Endorsement |
| Issuance | OAuth 2.0 (PAR, RAR) plus the OAuth binding: the approval event, the integrity anchors, the mission claim, with credential brokers as the custody plane |
| Decision | The runtime contract on AuthZEN 1.0, with ARAP and AROP for governed requests |
| Tool boundary | MCP tools/call as the PEP most builders already own |
| Lifecycle and evidence | Status pull, Signals push, the harness, SCITT audit transparency |
AuthZEN standardizes the decision. The runtime profile deliberately specifies invariants rather than a wire, and the AuthZEN profile is the interoperable PEP-to-PDP surface. ARAP turns a denial into a governed request, and the AuthZEN profile lets the PDP mark out_of_authority and approval_required denials as requestable so an agent can start narrow and ask for what it discovers it needs. This handbook calls that composition the discovery loop: deny, request, approve, expand, retry. A tool or resource discovered at runtime shows up as a requestable denial rather than as an error or an excuse for standing breadth. AROP, the AuthZEN Access Request OAuth Profile, a working group draft since August 2026, binds that workflow to OAuth completion for the token-side case. The Least-Privilege MCP series walks this per-call stack from the beginning, and the MCP application post shows both of its models becoming projections of one Mission.
Take Alice’s board-packet agent from the running example, halfway through its task and meeting ten resources it did not know about. They sort into three groups:
| Group | The resources | What happens |
|---|---|---|
| Already covered | Three further Q3 finance reports inside the query_financials entry | The PDP permits each call, and no approval runs |
| Expansion required | Four internal analytics and document stores the Authority Set does not name | Each first call is denied as requestable. The client gathers all four into one expansion Intent, and the Approver reviews one disclosure of the successor’s complete Authority Set (Expansion, Advanced) |
| Human review required | Two that would send the draft to outside auditors, and a partner’s data room behind another Authorization Server | External communication and cross-domain authority always go to a person under a template, a Progressive ceiling, or the Discovery profile (all three experimental) |
A standing consent can take the middle row without a prompt per resource. Under the Evaluate-only Progressive profile, if Alice consented at the outset to a ceiling naming internal read-only stores, a drawdown policy adjudicates each in-ceiling successor within published per-drawdown and per-chain rate bounds. For an agent doing its own work under service_owned or organizational authority, a governed_policy version a human approved (Advanced) can activate the discovered work as its own Mission beside the live one. It reaches a high-consequence class only through a committed exception that names the class and authorizes activation only (who may approve).
An expansion for authority the Mission already covers is refused as nothing_to_expand, and Expansion activates exactly one successor per predecessor and refuses a concurrent loser with superseded_by_concurrent_expansion, so related needs belong in one proposal. The Evaluate-only Open-World Discovery profile defines the encounter itself. The Mission Issuer pins each resource’s identity from its own retrieval, treats a resource’s self-description as a claim that never relaxes classification, and routes every new encounter to a person when the harness reports the session tainted. Deferred Approval limits concurrent pending proposals per client and Approver, Discovery requires a published per-Mission rate bound on encounter adjudications, and the AuthZEN profile asks deployments to rate-limit and anomaly-check synchronous auto-approval. The fatigue budget measures what gets through, and a resource that keeps turning up mid-task belongs in the derivation policy or under a standing consent, so the next Mission starts with it (adjusting policy from evidence). Missions make newly requested authority governable. The deployment still has to learn what each discovered resource’s operations mean, translate them into Authority Set entries, and decide when a person must be interrupted.
Two observations from the Least-Privilege MCP series matter for this adoption guide, because they name what the ecosystem still lacks:
- Fulfillment is undefined. ARAP standardizes the request, the status, and the re-evaluation, and deliberately not how an approval becomes durable authorization state. Token-resident state fulfills by minting, which AROP binds to OAuth issuance. Store-resident state fulfills by a write no standard defines. When the durable state an approval becomes is a Mission, fulfillment has a governed shape. An in-bounds approval is decision input, and a widening lands as a separately approved successor Mission with lineage.
- The task object is the gap every layer routes around. The denial signals, the decision API, and the approval workflows each standardize an interface inside a single call. None names the work the calls serve, and an object that names it is what this chapter proposes.
The identity substrate composes from below: AIMS’s best practices for agent authentication and authorization, the Actor Profile for delegation chains, and Client Instance Identification with Client Attester Endorsement for attributable instances. Instance evidence alone identifies no actor, so attribution also needs an instance-unique key. Mission-Bound Authority is the binding between that substrate and the Mission.
Credential custody composes the same way. Credential brokers are the custody fabric Baseline Issuance already put to work, and CB4A’s own future-work sketch, a native token carrying issuer, scope, expiry, and a confirmation key bound to an envelope hash, is reaching toward the mission claim.
Coexistence with the entitlement plane runs for years and needs a stated rule: the standing entitlement is the outer boundary, the Mission the inner one, derivation validates against what the underlying account currently holds, and a mid-Mission deprovisioning surfaces as a lifecycle event rather than a failure two systems disagree about. The gap between the two boundaries is the estate’s own measure of what the layer bought.
The roadmap: the next layer of the problem
The roadmap beyond the Runtime-Enforced level has two labels. They are the handbook’s adoption guidance, separate from the drafts’ own spec-maturity axis, on which 44 of the 52 documents are experimental. The advanced profiles are designs to adopt when the use case arrives, and the implementation chapter carries them: Deferred Approval and Intent Shaping (From a Request to an Approved Mission), Expansion, Entry Discharge, Lifecycle Signals, and the Mission Status List with the fleet Management surface (Mission Lifecycle and Change), Child Delegation and Cross-Domain Projection (Mission-Bound Authority), Audit Transparency (The Agent Runtime and Audit), and the Mandate.
The Evaluate only profiles are for evaluation. Each extension in the table answers a question Runtime-Enforced deployments will surface in production. Signals, in the first row, is advanced:
| Next-layer problem | Extension | Why it needs iteration | Today’s alternative |
|---|---|---|---|
| Revocation must bite in seconds | Mission Lifecycle Signals | Push is a latency optimization over correctly sized status polling | Status polling sized to the risk, or introspection |
| Reviewers narrow instead of denying | Mission Approval Revision | Companion to Deferred Approval, riding a substrate the OAuth working group adopted only in September 2026 | Deny, then resubmit a narrower Intent |
| Open-ended tasks need governed drawdown | Mission Progressive Authorization | Ceiling-and-drawdown is a newer model | Per-step Expansion with fresh approval |
| Budgets and call caps need runtime metering | Mission Consumption Metering | Cumulative-bounds enforcement is a newer model | Per-action constraint checks and short expiries |
| Fan-out at swarm scale without an issuer round-trip per delegation | Mission Offline Attenuation | Depends normatively on Attenuating Agent Tokens, an in-progress draft | AS-mediated Child Delegation |
| A Mission stops mid-workflow with work in flight | Mission Orchestration and Unwinding | Reversibility classes and unwind plans are less exercised | Harness stop behaviors, human review |
| The agent meets resources its approval could not name | Mission Open-World Discovery | Encounters adjudicated against a pre-consented ceiling, with the lying-resource and tainted-session floors, are a newer model | The discovery loop: deny, request, approve as a successor Mission |
Two profiles proposed for the Standards Track sit beside this table rather than in it, because each tracks a substrate that is still a draft: Deferred Approval rides OAuth Deferred Token Response (an OAuth working-group draft since September 2026), and the AAuth binding rides the AAuth protocol (an individual draft, at -11). The standalone Mission Authority Server is a proposed binding requesting the Standards Track, not a roadmap item, with the issuance grant as its middle path. The Authority Control Plane carries the trade this binding makes.
The Reference’s draft family at a glance is the whole 52-document catalog in one table, with these adoption labels on every row.
What you will operate
Adopting the Runtime-Enforced level means owning six things:
- Derivation policy. Someone maintains the policy that turns a
validated Intent into an Authority Set, per resource, the same
onboarding work scope design was. The record’s
policy_versionexists so a derivation can be re-checked, and the owner is typically the IAM team together with the resource owners. - The approval surface. The shaper is client-side and app-owned. The consent rendering and approval routing belong to the Mission Issuer, and Deferred Approval lets an existing request-and-approval workflow drive the decision.
- The PEP fleet. Gateways, MCP servers, egress proxies, and orchestrators each need a PEP at the last controllable boundary, owned by the platform teams that own those boundaries, with the enforcement-scope statement naming what is and is not covered.
- The PDP as a tier-0 dependency. Fail-closed means agents stop when the PDP is unreachable. The permit-as-lease model with published staleness bounds (Mission-Bound Runtime Enforcement) provides availability through bounded caching and never fails open. Mission state distributes as signed, TTL-bounded artifacts, the Status response and the fleet-scale Mission Status List, cacheable and servable from replicas the way a JWKS is, so the Issuer’s control plane can be briefly unreachable without the data plane losing its state source. The staleness bound you publish is also the longest outage you can ride, so choose it with the Issuer’s recovery objective in view. State the blast radius in the runbook rather than discovering it: an outage past the bound halts PDP-gated classes and only them, issuance-gated paths ride to token expiry, and the break-glass below is the named exception.
- The incident playbook. Revocation by
mission_idis the kill switch, Status is how consumers learn it (with the Signals push where seconds matter), and fleet-scale response (enumerate a compromised principal’s active Missions and bulk-revoke, dry-run first) is Mission Management’s job. - The break-glass path. Fail-closed is the design, so name the pressure valve before an outage improvises one: a dual-controlled emergency bypass that auto-expires, emits the same evidence as the path it bypasses, and suspends the runtime-enforcement claim for whatever it touches while active. A break-glass nobody designed becomes a standing unmediated path.
The derivation policy, concretely
The family fixes no policy language, because derivation policy is deployment policy. What the drafts fix is its contract. Derivation is mechanical, so the policy must be a deterministic function from a validated Intent and the registry’s facts to an Authority Set, with no discretion left for decision time. A model’s output can enter only as a recorded input, kept with the model’s identifier and version, that refuses or narrows. It never supplies or widens an entry, and a replay uses the retained output instead of rerunning the model.
The function consumes structured members only: the Intent’s purpose and target_resources, (in the editor’s copy) the requested scope values for a scope-only target, and any top-level authorization_details proposal submitted beside it, which proposal_hash commits as submitted. The Intent’s human-readable task_bounds bind at disclosure: they are what the Approver reads beside the derived authority, never what the function parses, and the AS derives the same set whatever they say. A bound the PDP must enforce enters as structure, in a proposed authorization_details entry’s machine-actionable constraints the shaper may translate from the request’s words and the AS only ever narrows (narrowing mode), or in the configured rule itself, authored by a human who read the same words (configured-mapping mode). “Q3 2026” becomes an enforceable period bound at one of those two doors, and the Approver’s check that the structure matches the words is what closes the gap between them.
The table shows one rule in the shape most estates will write it. The language is illustrative and the rows are the contract:
| The rule’s parts | This rule (finance read, board-packet class) |
|---|---|
| Matches when | target_resources names the finance service and the validated Intent’s purpose is in the reporting class |
| Registry facts consulted | The Agent Deployment’s eligibility bounds and risk tier |
| Emits | One mission_resource_access entry (the Resource Access Profile’s type): query_financials, read-only, with the fiscal-period bound sourced from the rule or the structured proposal, never parsed from task_bounds |
| Never emits | Write actions, exports, or any entry for a resource the Intent did not name |
| Notices | The data-classification notice class, so the disclosure renders it |
Testing is fixtures, the same discipline the disclosure templates
use: a corpus of representative Intents with their expected Authority
Sets, run on every policy change, with the diff reviewed like a code
change, and policy_version on each record pointing at exactly which version derived what. That pointer is also the recall mechanism. When a derivation version is found faulty, recall is a query against a deployment-maintained index, and every Mission derived under that version can be enumerated and suspended as a class. Mission Management does not yet standardize selection by policy version. Ownership follows the two vocabularies. The IAM
team owns the function and the ceilings. Each resource owner owns the
entries that touch their service, because
the resource owns the meaning.
The authoring surface is scope design’s workload relocated, with better economics and a real cost. The surface is bounded by resources and action classes rather than by integrations, it is populated once per resource and amortized across every Mission that touches it, and templates (the experimental Template profile) are where the common cases stop needing new authoring. Watch three numbers the way the fatigue budget watches its four: the unmapped-resource rate (Intents that fail derivation because no rule exists), the template-hit rate (how much work rides pre-approved shapes), and the rule-exception rate (policy edited under deadline, the tell that the ontology is wrong).
Templates are where derivation policy and the approval surface meet operations. The mock below shows a catalog of pre-reviewed mission shapes with risk and duration visible, governed by the policy framework, where new templates enter through policy review rather than around it:
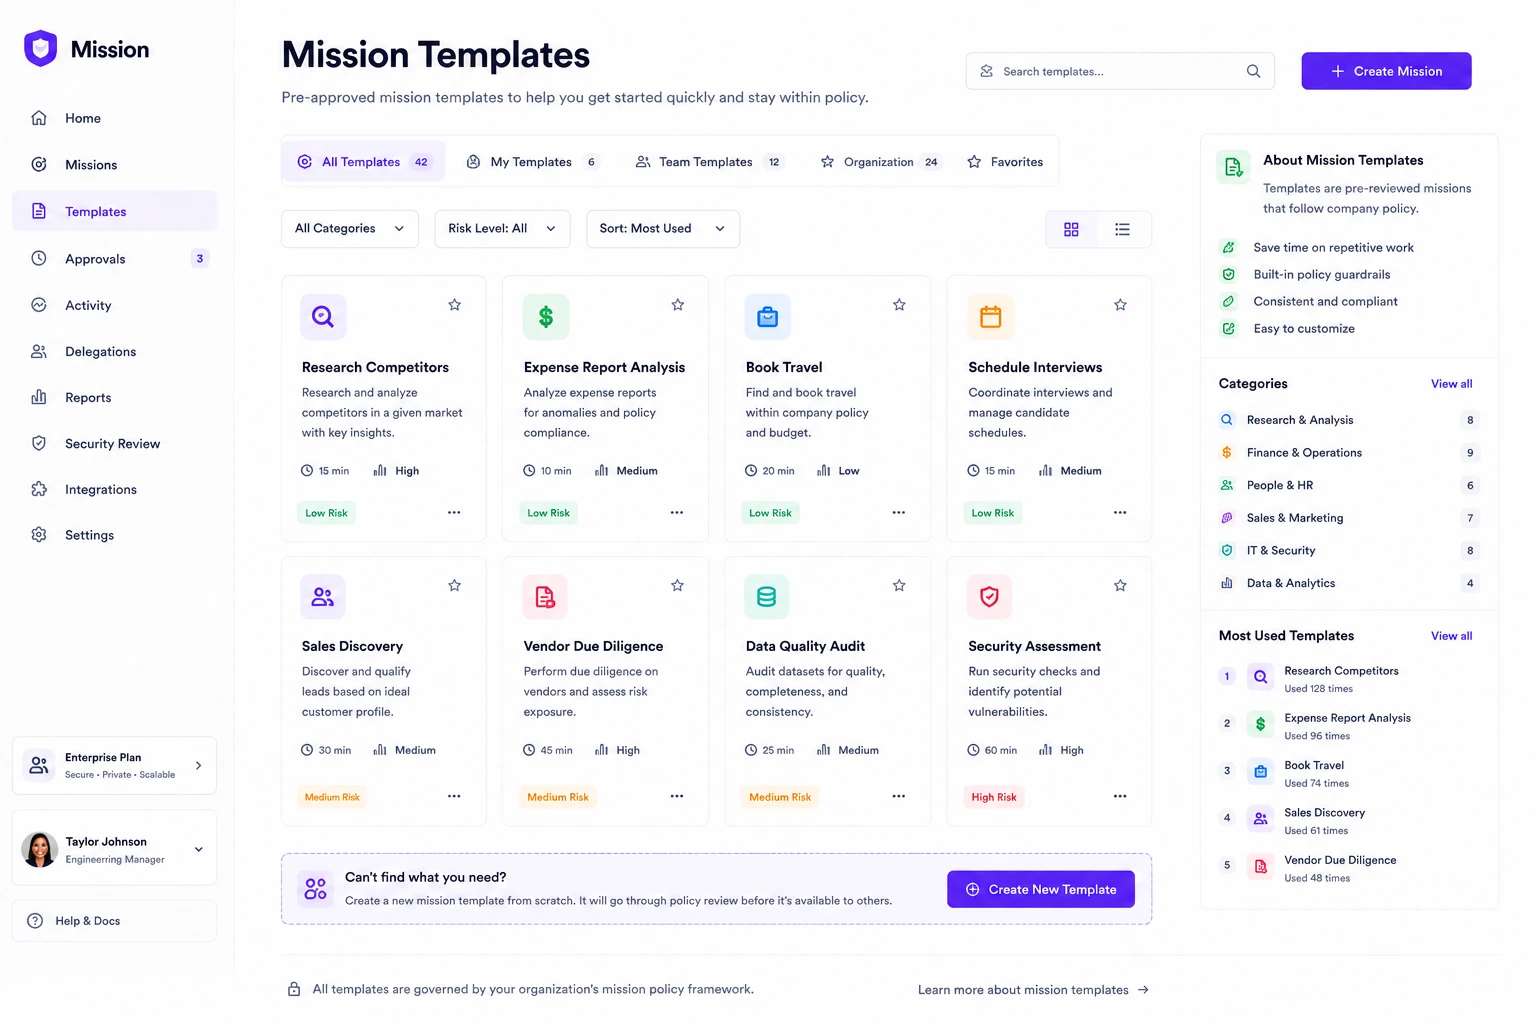
The signing keys ride with all six surfaces. The Mission is a durable record rather than a token in flight, so an issuer key rollover invalidates projections and signed status while the records survive, and every projection re-derives under the new key. Key custody and a rehearsed recovery drill belong in the enforcement-scope statement, and the drill’s measure is the time back to governed operation.
Adjusting policy from evidence
Review decision and execution records, consumption where it is metered, approval workload, denials, exceptions, and the three derivation rates above on a regular cadence, joined to the Missions and policy versions that produced them. An issuance-only deployment has approval, issuance, and lifecycle evidence. Action-level conclusions need execution telemetry that can be reliably joined to the Mission, which ordinary resource or broker logs may provide. Missing coverage limits what the review can conclude.
Authorized policy can suspend a Mission through the lifecycle surfaces, and narrow one where the deployment runs the Evaluate-only containment profile. Evidence never authorizes a broader grant by itself. A human consents to a broader template or ceiling, or approves a policy change, and later activations still follow the applicable approval and lifecycle rules. Inside an envelope a human already consented to, policy may adjudicate eligible instances and successors. A new policy version does not enlarge an existing Mission’s committed Authority Set.
| Evidence | Response |
|---|---|
| Suspicious decisions, consumption, or egress | Suspend, or contain where containment is deployed, keeping the evidence and naming the recovery authority |
| Near misses, bounds a resource could not check, or a revocation bound that proved too slow | Tighten policy or freshness, or put the path under runtime enforcement; update the enforcement-scope statement and verify the new bound |
| A faulty derivation rule | Enumerate the Missions its policy version derived, and suspend or review them |
| A standing ceiling (Evaluate only) due for review | Renew at the envelope the evidence shows was used; anything wider is a new approval (the standing agent at scale) |
| Repeated work with a reviewable record of authority used, exceptions, and outcomes, and no high-consequence, external-communication, or cross-domain authority | Ask a human to consent to a template or a ceiling (both Evaluate only) for it, or to approve a governed_policy adjudication policy, which can also complete pending Deferred Approvals and leaves an evaluation that does not activate to a human’s direct approval or a denial |
The review applies to every class. It can tighten high-consequence paths but never replaces their pre-action controls, because approving fast and reconciling later is tuned wrong for irreversible verbs. The ceiling review is the control plane’s reconciler for this evidence. Fleet-wide consumption and denial queries, and comparing consumption with the time a Mission has left, have no standard form yet.
What the community still has to standardize
Six pieces have no owner yet:
- A standard task object. This family proposes one, as individual drafts published for discussion. The gap it fills is now named in AIMS, a WIMSE working-group document, and the per-call standards keep converging on shapes that assume something like it exists. Working groups are wary of a large family from one author, so the proposed standardization surface is three documents: the informative Architecture (the model), the normative Substrate Requirements (the binding-neutral kernel contract), and the OAuth binding. Everything else, the runtime profiles included, is companion work on its own timeline that enters scope only as the community pulls it. The author’s proposed initial OAuth working-group conversation is narrower, the OAuth binding (-01) and the Resource Access Profile (-00) on the datatracker, and the Reference’s draft-family section sets it beside the other scopes. Which venues take up the rest, the OAuth working group, AuthZEN, or both, is the next conversation, and deployment experience is the strongest input anyone can bring to it.
- Approval fulfillment for store-resident state. Every Zanzibar-style store’s write API is product-specific. A Mission gives the durable state a governed shape, but the write itself still needs a standard.
- Task binding at the tool boundary. The MCP proposals standardize the denial and the brokered approval. Carrying a verifiable task reference through
tools/call, so the resource can weigh the call against the approved work, is the natural next step the MCP application post sketches. - Instance-attested delegation as the default. The actor chain, client instance identification, and attester endorsement exist as proposed individual drafts. The mission layer assumes them. Their adoption belongs in this guide, because an unattributable actor makes every downstream guarantee weaker.
- Trust establishment for discovered counterparties. The Mission layer governs whether newly requested authority is inside the approved task. Whether a runtime-discovered issuer, tool server, or its metadata can be trusted at all is the substrate problem beneath it, and the Open-World OAuth series maps that terrain: discovery, issuer trust, sender constraints, and metadata integrity are prerequisites this guide composes with rather than solves.
- Exposure control surfaces. Least privilege has standards, and least exposure does not yet. Bounding what the agent may see is enforced today only at its edges (catalog filtering, egress mediation, the taint rule). Scoping retrieval, memory, and context assembly to the approved task has no interoperable form, and the exposure half of minimal disclosure needs profile work nobody has started.
Where this leaves you
If you arrived from AIMS, you now have the answer to the question its Agent Mission section leaves open. The Mission is the durable, approval-backed record of the task your authenticated agent pursues. Choose the entry point your estate supports, then add the controls needed for the claims your deployment must make.
The Building Mission-Bound Authorization chapter carries each control at implementation depth, the editor’s copies are public, and the Reference is the citable definition. Issues and pull requests on the draft repository are the fastest way into the documents for deployment experience.